
Knowledge Base
Community Blog.
Security research, CTF writeups, and technical articles authored by our members and reviewed by the admin team.

"AI in cybersecurity: How AI become both shield and weapon?"
Learn how AI in cybersecurity powers deepfake scams, prompt injection and polymorphic malware, and how defenders use AI to fight back and keep you safe.
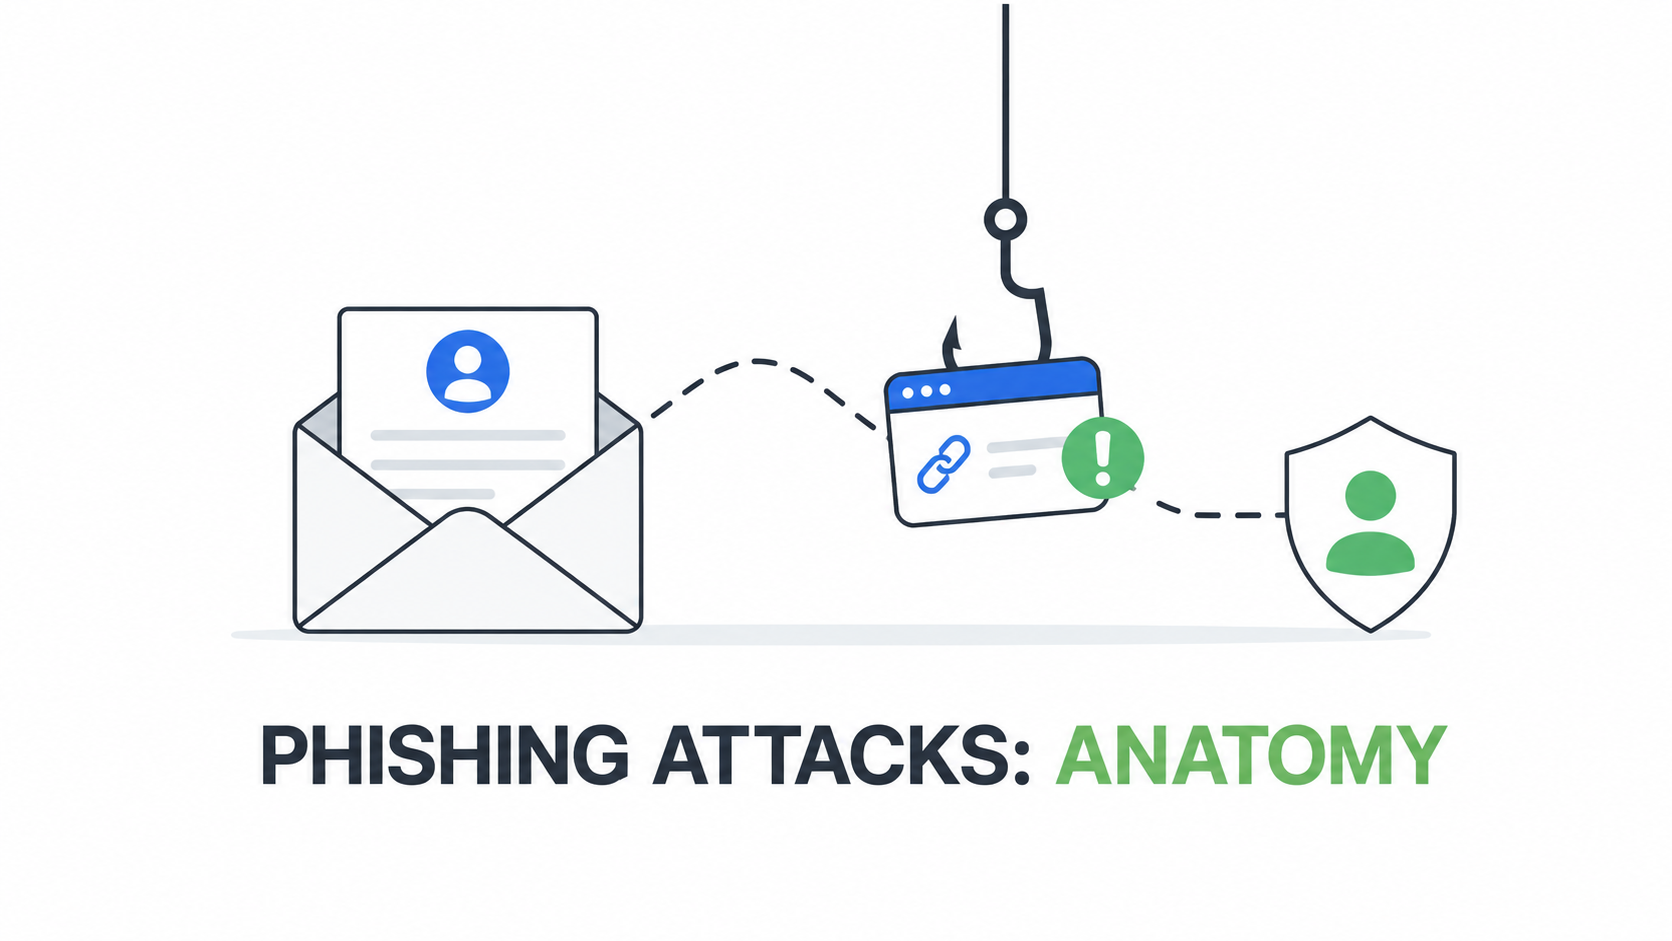
How Phishing Attacks Trick People: An Anatomy of Phishing
Phishing is more than a fake email. Learn how attackers build trust, create urgency, capture information, and how users and organizations can stop the attack.
Burp Suite Lesson 3: Broken Access Control × Burp Suite
Learn the basics of Broken Access Control and discover how attackers can exploit access control flaws using Burp Suite through hands-on practical labs.
Social Engineering: When Attackers Exploit People
This blog is about social engineering—how psychology and trust are exploited through phishing, impersonation, BEC, and MFA fatigue.
What Really Happens When You Enter a URL in Your Browser?
Ever wondered what happens after you press Enter? Follow a URL from DNS lookup through TCP, TLS, HTTP, the server, and finally back to your browser.
Burp Suite Lesson 2 : Exploring Burp Suite Features
Exploring Burp Suite Features introduces Proxy, Target, Repeater, and Intruder for intercepting traffic and testing vulnerabilities.
How Hackers Discover Web Application Vulnerabilities
A practical beginner’s guide to web reconnaissance, attack-surface mapping, endpoints, parameters, technologies, Burp Suite, Nmap, and security testing.
Burp Suite Lesson 1: Essential Web Fundamentals
This beginner-friendly guide covers Burp Suite fundamentals and essential web security concepts before moving to practical labs.